Vendor Data Security
You are holding other companies’ information
Supplier onboarding collects tax identifiers, banking details, insurance documents and signed attestations, and none of it belongs to you. That is worth taking seriously, and it is worth being able to explain rather than gesturing at a badge.
Fewer moving parts, and a record you cannot quietly edit
Security conversations tend to jump straight to certifications. The practical questions are simpler: who can reach it, what happened to it, and can you get it back.
Fewer people can reach it than you think
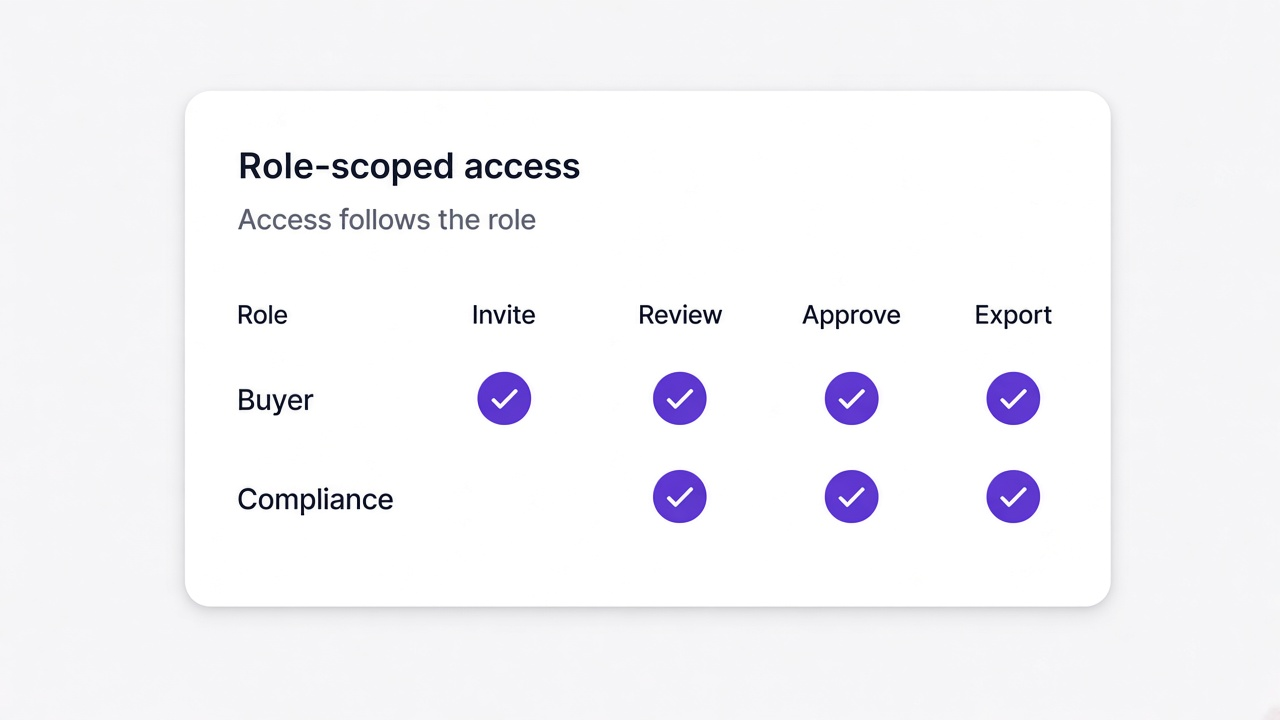
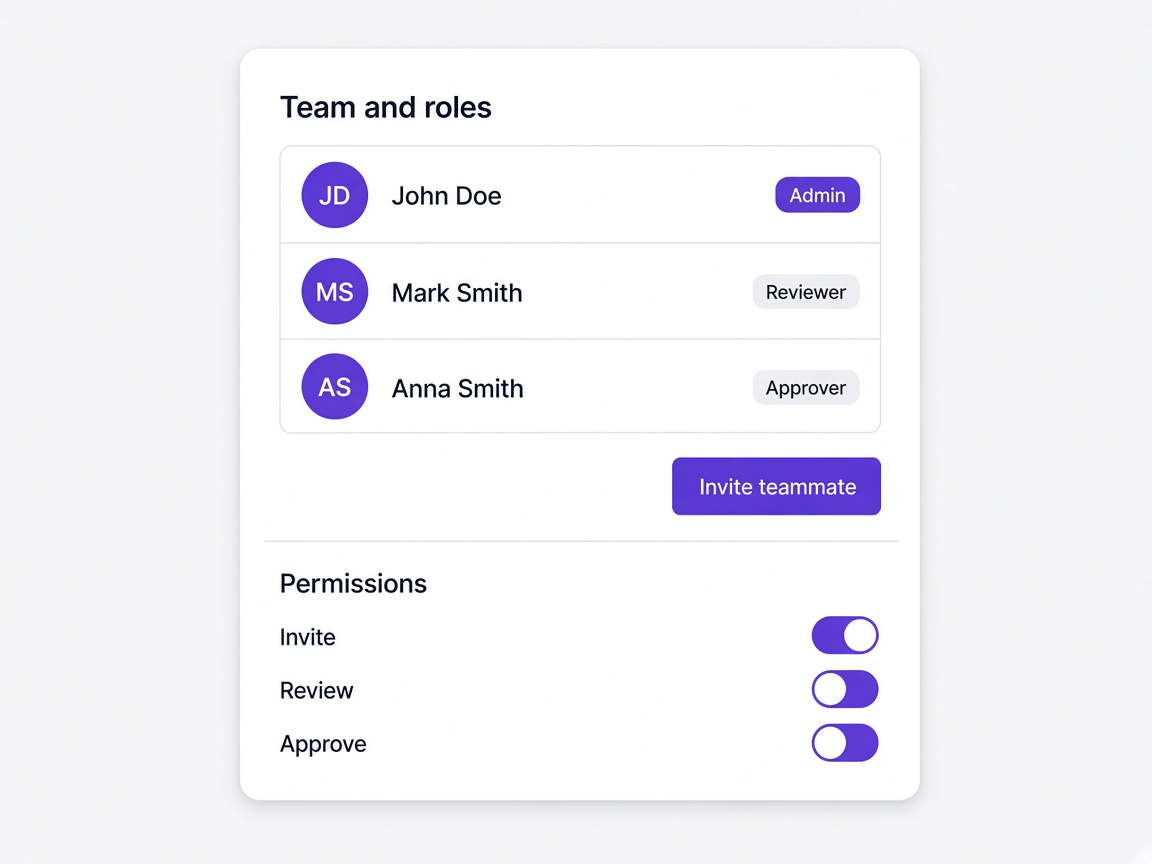
Access is scoped by role rather than granted per person, so the number of people who can see banking details is a decision rather than an accumulation.
Nothing changes without a trace
Entries are recorded as work happens and corrections are added rather than overwriting what was there, so the sequence of events holds its shape.
The data stays yours
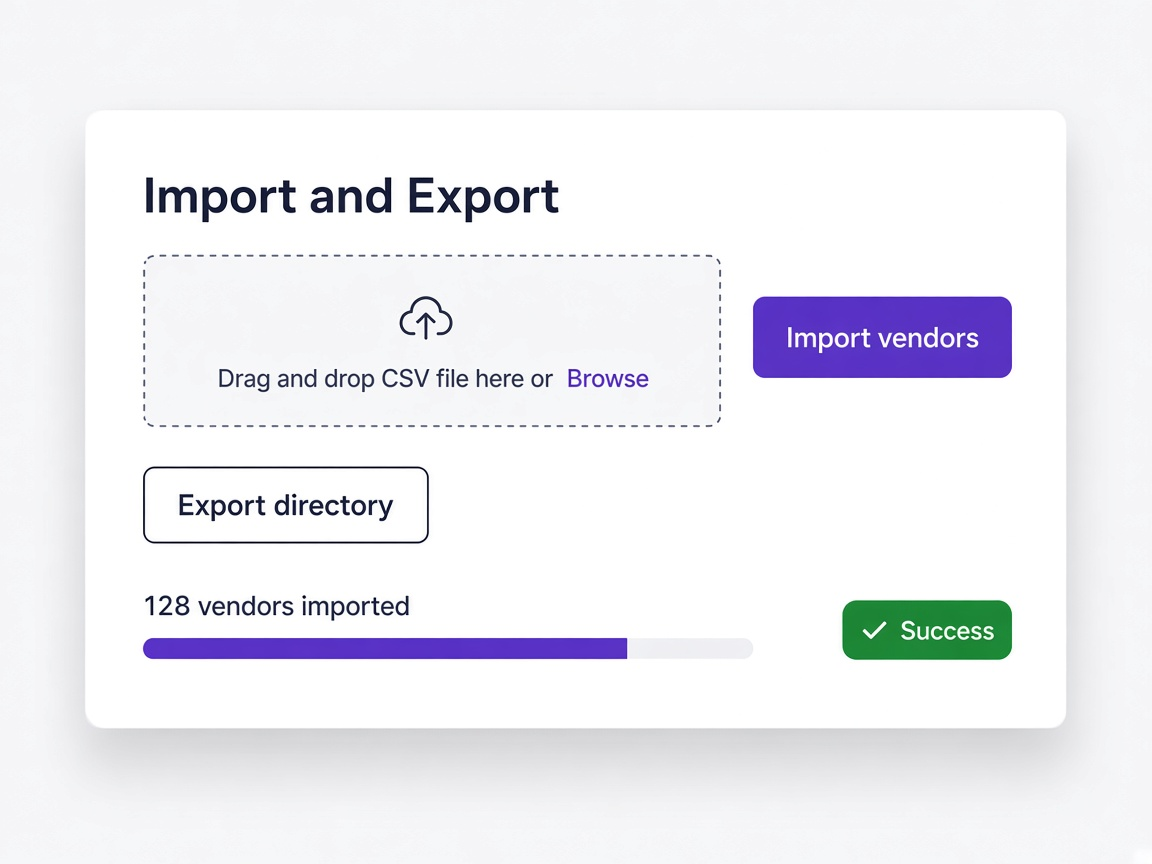
The directory, the documents and the scores export in full. Supplier information is used to qualify suppliers for you and nothing else.
Ours included
These are the four we would ask, and we would rather answer them plainly than point at a logo.
Whoever has a login
Access is broad by default and narrowed later if somebody raises it, which means the answer to who can see banking details is usually more people than intended.
Whoever the role allows
Roles carry their scope and people sit in roles, so the population who can reach sensitive fields is deliberate and reviewable.
A current state
The system shows what a record says now, and what it said last month is not recoverable, so mistakes and changes look identical.
A recorded sequence
Actions are recorded as they happen and corrections are added as further entries, so what changed and when is visible.
Another account
Every supplier account is another credential to be reused, shared or lost, and a portal full of them is a larger surface than it looks.
Nothing at all
Suppliers work from a secure link with no account and no password, which removes a whole category of credential problem.
A support request
Export is limited or partial, which is a commercial position rather than a technical one, and it is worth discovering before you commit.
A file, whenever you like
The directory exports in full with scores, categories and document links, and we would encourage you to test it during evaluation.
Questions worth putting to us directly
Who in our team can see banking details
Answered by naming the roles that carry that access rather than counting logins.
Learn moreWhat did this record say in March
Answered from the recorded sequence rather than the current state.
Learn moreWhat happens when our administrator leaves
Access removed, their entries still attributed, no gap in the history.
Learn moreCan we take our data with us
Yes, in full. Worth testing during evaluation rather than afterwards.
Learn more